Student / community
LCSP Network Architecture
The lab's network — two stacked Catalyst switches, VLAN segmentation, ACLs and secure remote access over VPN.
My contribution
I design and run the LCSP network with my fellow infrastructure co-lead, working directly on VLANs, trunks, ACLs, routing and the Catalyst stack. I am gradually taking over a growing share of the network scope and am currently leading a major overhaul of the switch configuration.
Highlights
- Two stacked Cisco Catalyst 3850 switches, behind a UniFi gateway
- VLAN segmentation — administration, guests, isolated lab environments
Goal
Connect the lab’s infrastructure and control access to its services.
Architecture
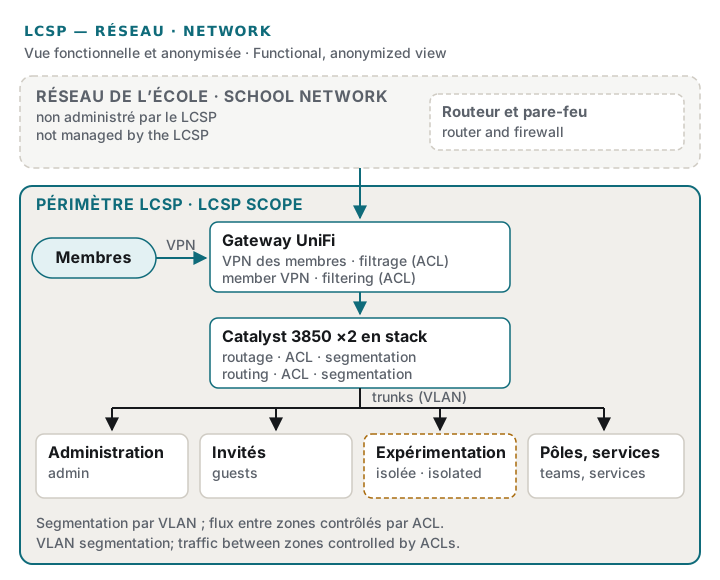
Two Cisco Catalyst 3850 switches run as a stack. Upstream, a UniFi gateway provides members’ remote access over VPN and part of the filtering. The connection to the outside goes through SUPINFO’s infrastructure: the school’s router and firewall are not managed by the lab.
Segmentation
The network is split into VLANs by use: administration, guests, isolated lab environments and different teams. Trunks carry these VLANs between devices, and ACLs, on the gateway as well as on the switches, control traffic between zones.
The addressing plan is structured so that an address range immediately tells which category of device or member it belongs to, which also makes monitoring easier.
Work in progress
A major overhaul of the Catalyst configuration is under way.
What is not published
No usable topology, addressing plan or VPN configuration: this page is deliberately kept general.